 Busirank Team
Introduction
AI marketing tools have become genuinely useful for small businesses. They write email campaigns, route leads, summarize calls, personalize offers, and surface customer insights that would take hours to find manually. They also create a new set of privacy obligations that most small business owners were never trained to manage.
The risk is not hypothetical. AI marketing systems often connect website forms, CRM, email, analytics, and advertising accounts—and each connection can copy customer records into places no one on the team regularly reviews. A chatbot may pull from CRM notes, a voice receptionist may create call summaries, and an analytics platform may link browsing behavior to an email address. Once a customer message, health detail, or payment issue is pasted into a public AI prompt, a privacy policy cannot undo it.
This guide explains how to protect customer data when using AI marketing tools. You will learn the common risks, how to handle consent and training data, how to vet vendors, and how to build a repeatable AI marketing data privacy workflow that fits a small business budget and team size.
1. Understand the Specific Data Risks AI Marketing Tools Create
AI marketing tools rely on data, which makes privacy a core operational concern—not a legal afterthought. The most common risks are consistent across tool types.
Common AI marketing data risks:
- Using personal data without proper consent.
- Training AI on customer or employee data improperly.
- Retaining data longer than allowed.
- Sharing data with third-party AI vendors.
- Transferring data across borders.
Source: Boyer Law Firm
For local businesses, the risk is compounded by how much customer data now flows through marketing systems. Marketing data collection covers more than names and email addresses—it can include phone numbers, IP addresses, website behavior, purchase history, SMS replies, call recordings, chat transcripts, appointment details, and ad audience lists.
Fix: Treat AI marketing data privacy as its own workflow. Do not assume your existing privacy policy covers what happens when data enters an AI tool. It usually does not.
2. Map What Data Your AI Tools Actually Touch
Before you can protect customer data, you have to know where it lives and how it moves. Most small businesses discover that AI tools are connected to more data than expected.
A practical data-mapping exercise:
- Inventory every AI marketing tool, integration, data source, and downstream recipient so you know what customer information is collected and shared.
- List the data types each tool processes: contact details, purchase history, communication logs, call recordings, browsing behavior, and inferred attributes.
- Identify where data is stored and processed, including whether it leaves your country or region.
- Note which tools receive more data than their task requires—a common source of unnecessary exposure.
AI can also infer sensitive patterns from non-sensitive data. Repeated purchases may suggest health status, financial stress, or personal circumstances. This means privacy is not only about credit cards—it is about inferences.
Fix: Build a simple data map in a spreadsheet: tool name, data types it receives, purpose, storage location, and vendor contact. Review it whenever you add or change a tool.
3. Apply Data Minimization Before Data Enters AI
The safest customer data is the data you never store or send. Data minimization is the single most effective privacy control available to a small business.
Minimization practices:
- Collect only what supports a clear purpose—for example, replenishment forecasting, not “everything we can get”.
- Limit what each AI tool can access. A chatbot does not need full CRM notes to answer a question about store hours.
- Use role-based access so only staff who need customer data can see it.
- Anonymize or aggregate data where the task allows it.
- Set retention limits and delete data you no longer need.
Fix: Before connecting a new AI tool, ask: “What is the minimum data this tool needs to do its job?” Configure access accordingly, rather than granting full account permissions by default.
4. Get Consent That Matches the Actual Use
Generic consent does not cover invasive uses. Consent obtained for one general purpose cannot be stretched to cover materially different and more sensitive data practices. The more invasive the collection, the more specific and conspicuous the consent must be.
This principle matters for AI marketing because AI often repurposes data in ways customers did not anticipate. Loyalty data collected for rewards should not quietly become training data for unrelated uses.
Consent practices that work for small businesses:
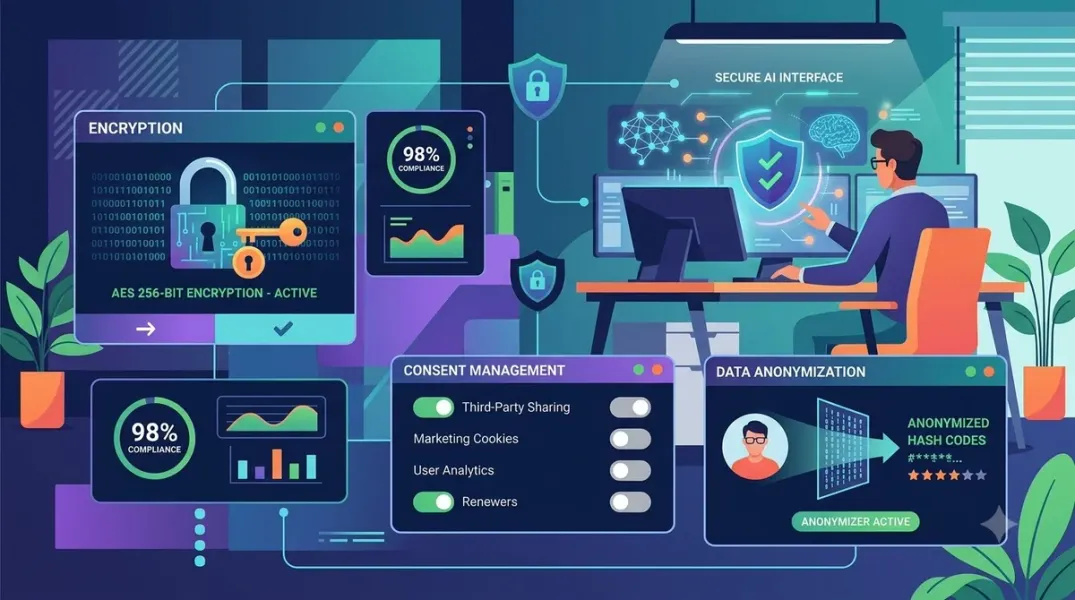
- Use plain language at the point of collection: what you will use the data for, how customers can control it, and what you will not do.
- Offer a preference center where customers can choose email vs. SMS, frequency, and whether they want personalized offers.
- Keep cookie and tracking consent readable if you sell online.
- Make opt-out functional at the point of purchase and honor requests within required timeframes. Under CCPA, opt-out mechanisms must be functional at purchase time and honored within 45 days.
Fix: Review your consent language specifically for AI uses. If you use customer data to train or improve AI models, say so clearly and provide a way to opt out.
5. Check and Change Training-Data Settings
One of the most overlooked AI privacy issues is whether a tool uses your customer data to train its models. Many commercial AI tools may use customer data for training by default, and the settings are often buried in account preferences.
What to check:
- Does the vendor use your inputs to train models? Look for phrases like “data training,” “data retention,” and “data sharing” in the privacy policy.
- Can you opt out? Many tools provide an opt-out in privacy settings. For example, HubSpot lets super admins turn off the AI model training switch in account AI settings. ChatGPT Pro and Plus users may have their interactions used for training by default but can opt out via the privacy portal.
- Does the opt-out apply to all data types, including connector data and CRM records?
Fix: Toggle the opt-outs on the tools you use most, and document which tools allow training opt-outs and which do not. If a vendor does not offer a clear opt-out, treat that as a risk factor in vendor selection.
6. Vet Vendors and Understand Your Contracts
Many small businesses rely on third-party AI platforms, which means vendor management is privacy management. Without proper contracts, your business may be held responsible for vendor failures.
Vendor vetting questions:
- What data does the AI collect or process, and does your privacy policy disclose it?
- Have you read the vendor’s data processing terms?
- Do you have a Data Processing Agreement with the vendor?
- How is data stored, secured, and retained?
- Does the vendor use subprocessors, and are they disclosed?
- What are the deletion and customer-rights support processes?
- Does the vendor offer compliance certifications such as SOC 2, HIPAA, ISO 27001, or GDPR? An enterprise tier may offer end-to-end encryption and these certifications.
Fix: Create an approved-software list of tools that have gone through privacy vetting, and require a DPA before any tool receives customer data.
7. Keep Sensitive Data Out of Public AI Prompts
The most direct privacy failure in AI marketing is also the easiest to prevent: staff pasting sensitive customer information into public generative AI tools. A privacy policy cannot undo a prompt that already sent an unredacted customer message, health detail, or payment issue to an outside AI model.
What should never go into a public AI prompt:
- Customer names, phone numbers, addresses, or government identifiers.
- Health information or medical details.
- Payment or financial data.
- Private social media messages or Google Business Profile messages.
- Unedited call transcripts.
- Legal questions involving a specific customer.
Source: Personal Data Protection practice guidance and small business AI security guidance
Fix: Write a one-page acceptable use policy that is specific enough to be actionable, and train staff on it. Set a clear rule: when in doubt, redact or do not paste.
8. Match Privacy Practices to the Laws That Apply
Data privacy regulations often depend on where your customers live, not where your business is based. A local business that markets across state lines or to international customers may be subject to multiple frameworks.
Key frameworks for small businesses:
- GDPR: Requires a lawful reason to process personal data. Consent must be clear, informed, specific where required, and easy to withdraw. GDPR fines can reach €20 million or 4% of global revenue.
- CCPA/CPRA: Requires opt-out mechanisms and honors data subject requests. Statutory damages remain 7,500 per violation, and opt-outs must be honored within 45 days.
- State privacy laws: Nearly two dozen states have passed their own data privacy laws, and some require disclosure when a user interacts with an AI-driven chatbot rather than a human.
- EU AI Act: Came into full force in 2026 and requires transparency, consent, and bias auditing for covered AI systems.
Fix: Match your consent, disclosure, opt-out, access, and deletion processes to the laws that apply where your customers live, including GDPR, CCPA, CPRA, and other state privacy laws. Do not assume a single generic policy is sufficient.
9. Build a Repeatable Privacy Checklist
Small businesses do not need a legal department to improve control, but they do need a repeatable review process.
A practical AI marketing data privacy checklist:
- Inventory: Every AI tool, integration, data source, and downstream recipient is documented.
- Minimization: Each tool receives only the data its task requires.
- Access: Role-based access is configured, and former staff are removed promptly.
- Retention: Retention limits are set, and data is deleted when no longer needed.
- Consent: Consent language matches the actual data use, including AI and training uses.
- Training opt-outs: Opt-out settings are reviewed and toggled where available.
- Vendor review: DPAs are in place, subprocessors are disclosed, and security certifications are verified.
- Sensitive data rule: Staff know not to paste customer data into public AI prompts.
- Customer rights: Access, deletion, and opt-out requests are handled within required timeframes.
- Recurring review: The inventory, policies, consent settings, and vendor reviews are updated whenever tools, purposes, or data-sharing practices change.
Fix: Assign one person to own the checklist and review it quarterly. A one-page policy with clear rules is more effective than a long document nobody reads.
10. Establish Human Oversight for AI-Generated Marketing
Privacy protection is not only about data handling. It is also about what AI says and does with customer-facing content. Small businesses using AI for sales and marketing should establish a strict human-in-the-loop oversight framework alongside clear data privacy guardrails.
Generative tools can misstate facts, compromise brand voice, or inadvertently leverage copyrighted material. No customer-facing asset should go live without human review. Poor AI governance is an immediate danger to profitability, and a single fine or refund associated with an uneducated chatbot can result in a major loss of profit for a small company.
Fix: Create a tiered review system: routine content reviewed quickly, and any offer, claim, or customer-facing AI interaction reviewed more carefully. Human oversight is a privacy safeguard as much as a quality safeguard.
Conclusion
Protecting customer data when using AI marketing tools is not about avoiding AI. It is about controlling what data enters the system, how it is used, who can see it, and how long it is kept. The risks—improper training, excessive retention, vendor exposure, and sensitive data in public prompts—are well documented and largely preventable.
Small businesses have a practical advantage here: fewer tools, shorter approval chains, and the ability to adopt good practices before bad ones become entrenched. By mapping your data flows, minimizing what AI tools can access, fixing consent and training opt-outs, vetting vendors, keeping sensitive data out of public prompts, and reviewing everything on a quarterly rhythm, you can use AI marketing tools without turning customer trust into a liability.
Call to Action
Is your AI marketing stack protecting customer data—or quietly exposing it? Start with a simple inventory: list every AI tool connected to customer data, check its training-data settings, and confirm you have a data processing agreement in place. If you want a structured review of your AI marketing privacy practices, contact us for a free AI data privacy checkup and get a prioritized plan for closing gaps before they become problems.
FAQs
Q1: What is AI marketing data privacy?A: It is the practice of controlling what customer information AI marketing tools can collect, share, infer, and retain—so you can use AI while protecting customer trust and meeting legal obligations.
Q2: Do AI marketing tools use my customer data for training by default?A: Often, yes. Many commercial AI tools may use customer data for training unless you change the settings. Check your account’s privacy and AI settings, and look for a training-data opt-out.
Q3: Can I paste customer information into ChatGPT or other public AI tools?A: No. Never put customer names, phone numbers, health details, payment data, or unedited call transcripts into a public AI prompt. A privacy policy cannot undo a prompt that has already sent sensitive data to an outside model.
Q4: What laws apply to AI marketing data privacy for a small business?A: It depends on where your customers live. GDPR applies to EU/EEA customers, CCPA/CPRA to California residents, and nearly two dozen U.S. states have their own privacy laws. Some states also require disclosure when users interact with an AI chatbot rather than a human.
Q5: Do I need a lawyer to protect customer data in AI marketing?A: Not necessarily. A repeatable checklist—data inventory, minimization, consent review, vendor vetting, training opt-outs, and human oversight—covers most day-to-day risks. Legal review is most valuable when you handle sensitive data, serve customers in multiple jurisdictions, or sign large vendor contracts.
Grow Your Google Maps Ranking on Autopilot
Stop spending hours every week manually replying to customer reviews and writing Google posts. Busirank automates your Google Business Profile to boost your local SEO rankings and turn searchers into paying clients.
 Busirank Team